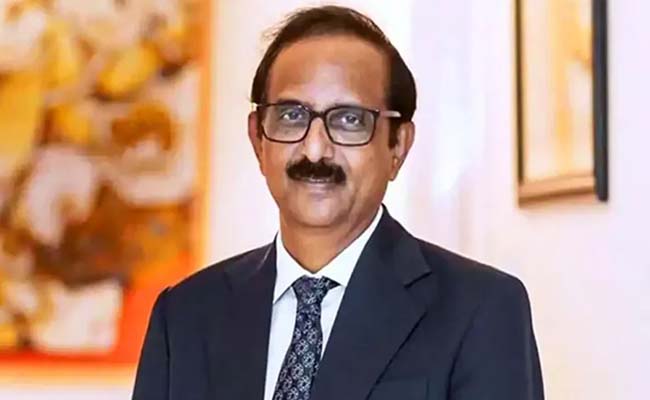
C S Setty,Chairman.SBI
SBI is also working with the banking industry to establish a common sandbox, or controlled testing environment, to evaluate artificial intelligence models and identify potential cybersecurity threats.
Mumbai: State Bank of India (SBI), the country’s largest lender, has pledged to strengthen its cybersecurity framework following a recent data breach that exposed 3,897 customer records on the dark web.
SBI is also working with the banking industry to establish a common sandbox, or controlled testing environment, to evaluate artificial intelligence models and identify potential cybersecurity threats.
SBI Chairman C S Setty said the incident had reinforced the bank’s resolve to strengthen its cybersecurity measures and prevent similar breaches in the future.
“Cybersecurity always has been of paramount importance for us. We are very conscious of our role to play in not only in ensuring that SBI systems are protected, customer data is protected, we are also working with other ecosystem players through the IBA to ensure that the BFSI sector comes together in ensuring that the cyber threats are handled in a better manner. We are also working on how AI can be adopted to fight the AI threats,” he told IANS.
“I think it (the incident) has strengthened our resolve further to ensure that our cybersecurity measures are strong enough to prevent any such breaches in future,” Setty said.
The bank is currently investigating the suspected cyberattack, focusing on containing the breach, identifying vulnerabilities and addressing gaps in its systems.
Setty said the root cause analysis was still underway and could take some time to complete.
Last month, SBI disclosed that 3,897 customer records containing sensitive personal information had been leaked on the dark web. A preliminary assessment indicated that the exposed data included customer names, mobile numbers, dates of birth, email addresses, residential addresses, brand and customer identifiers, and loan-related records.
The bank had said that the incident was not expected to have any material impact on its core business operations, financial performance or business continuity.
Setty’s remarks come at a time when India’s financial sector is stepping up its cybersecurity preparedness, with the Reserve Bank of India tightening cyber-risk monitoring and security requirements for lenders.
The SBI incident has once again highlighted the growing vulnerability of financial institutions to data breaches and the need for stronger safeguards as banking services become increasingly digital.
Setty said SBI remains highly conscious of its responsibility in protecting its systems as well as customer data.
He noted that cybersecurity has always been a critical priority for the bank and that it is actively engaging with other stakeholders through the Indian Banks’ Association (IBA) to ensure a coordinated response to cyber risks across the financial ecosystem.